Interpreting Results
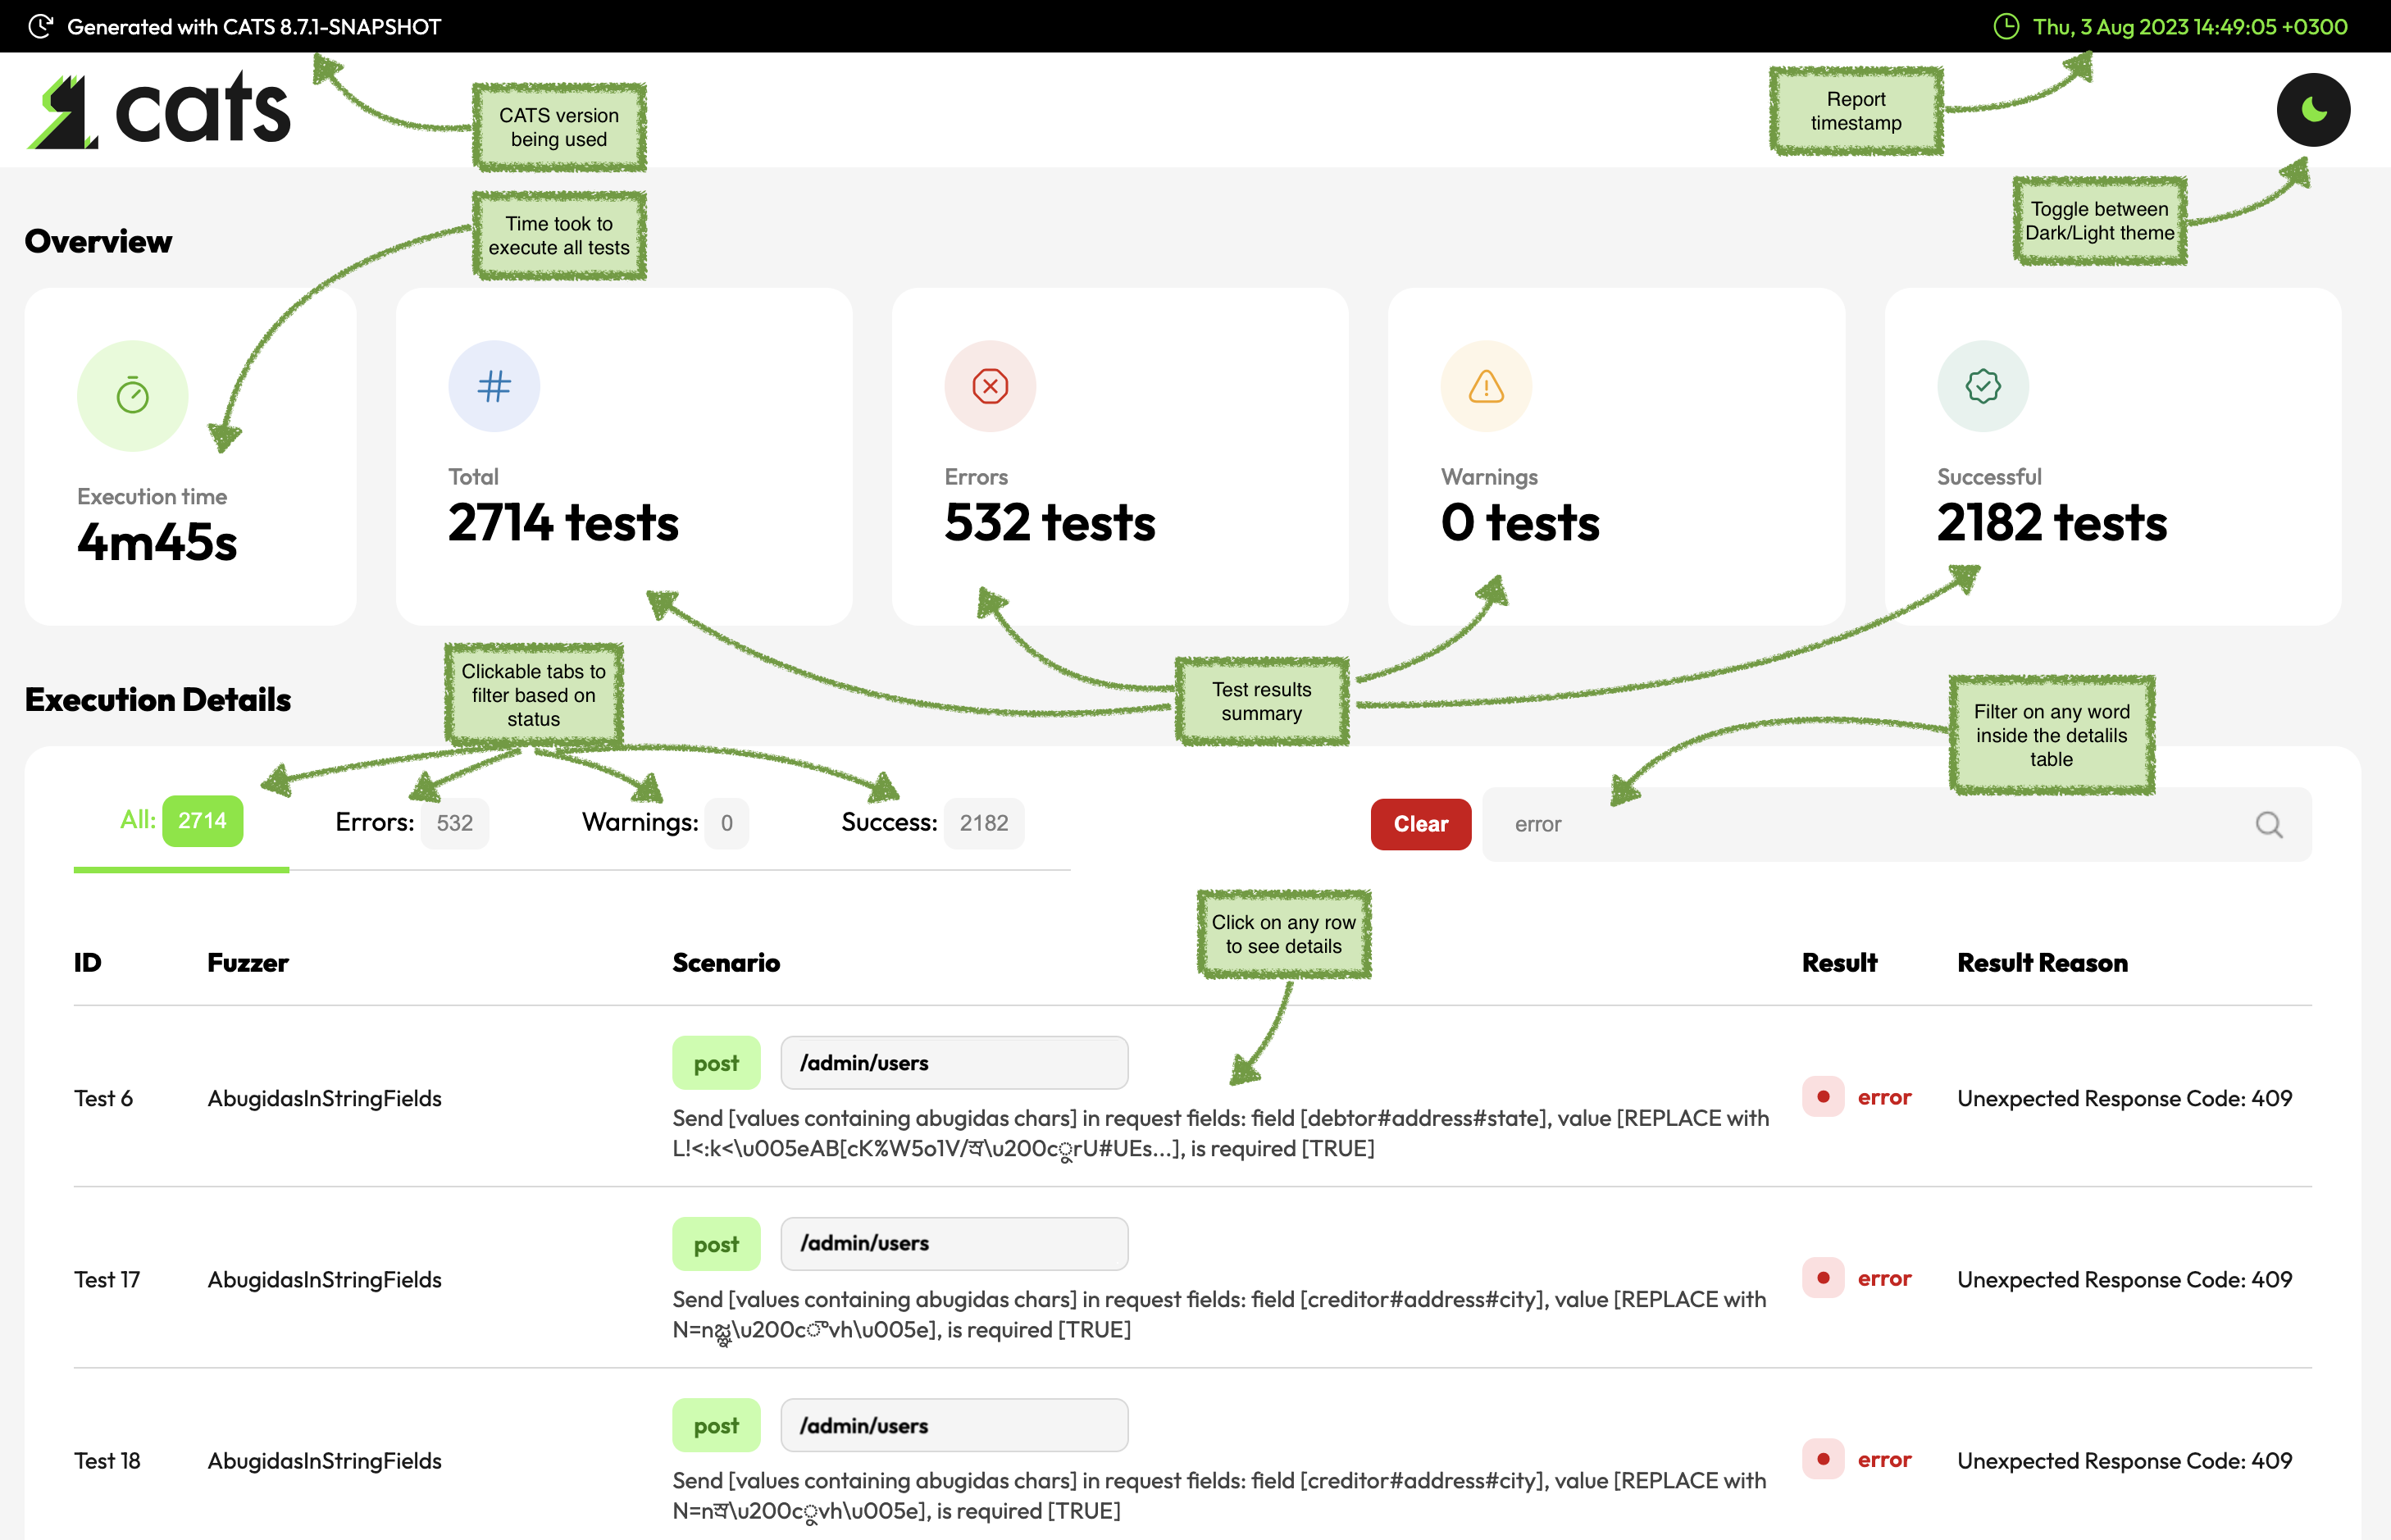
This is a typical CATS report summary page:
HTML_JS
HTML_JS is the default report produced by CATS. It has Javascript enabled in order to have some interaction with the reports.
The execution report is placed in a folder called cats-report which is created inside the current folder.
Opening the cats-report/index.html file, you will be able to:
- filter tests based on the result:
All,Success,WarnandError - omni-search box to be able to search by any string without the summary table
- see summary with all the tests with their corresponding path against they were run, and the result
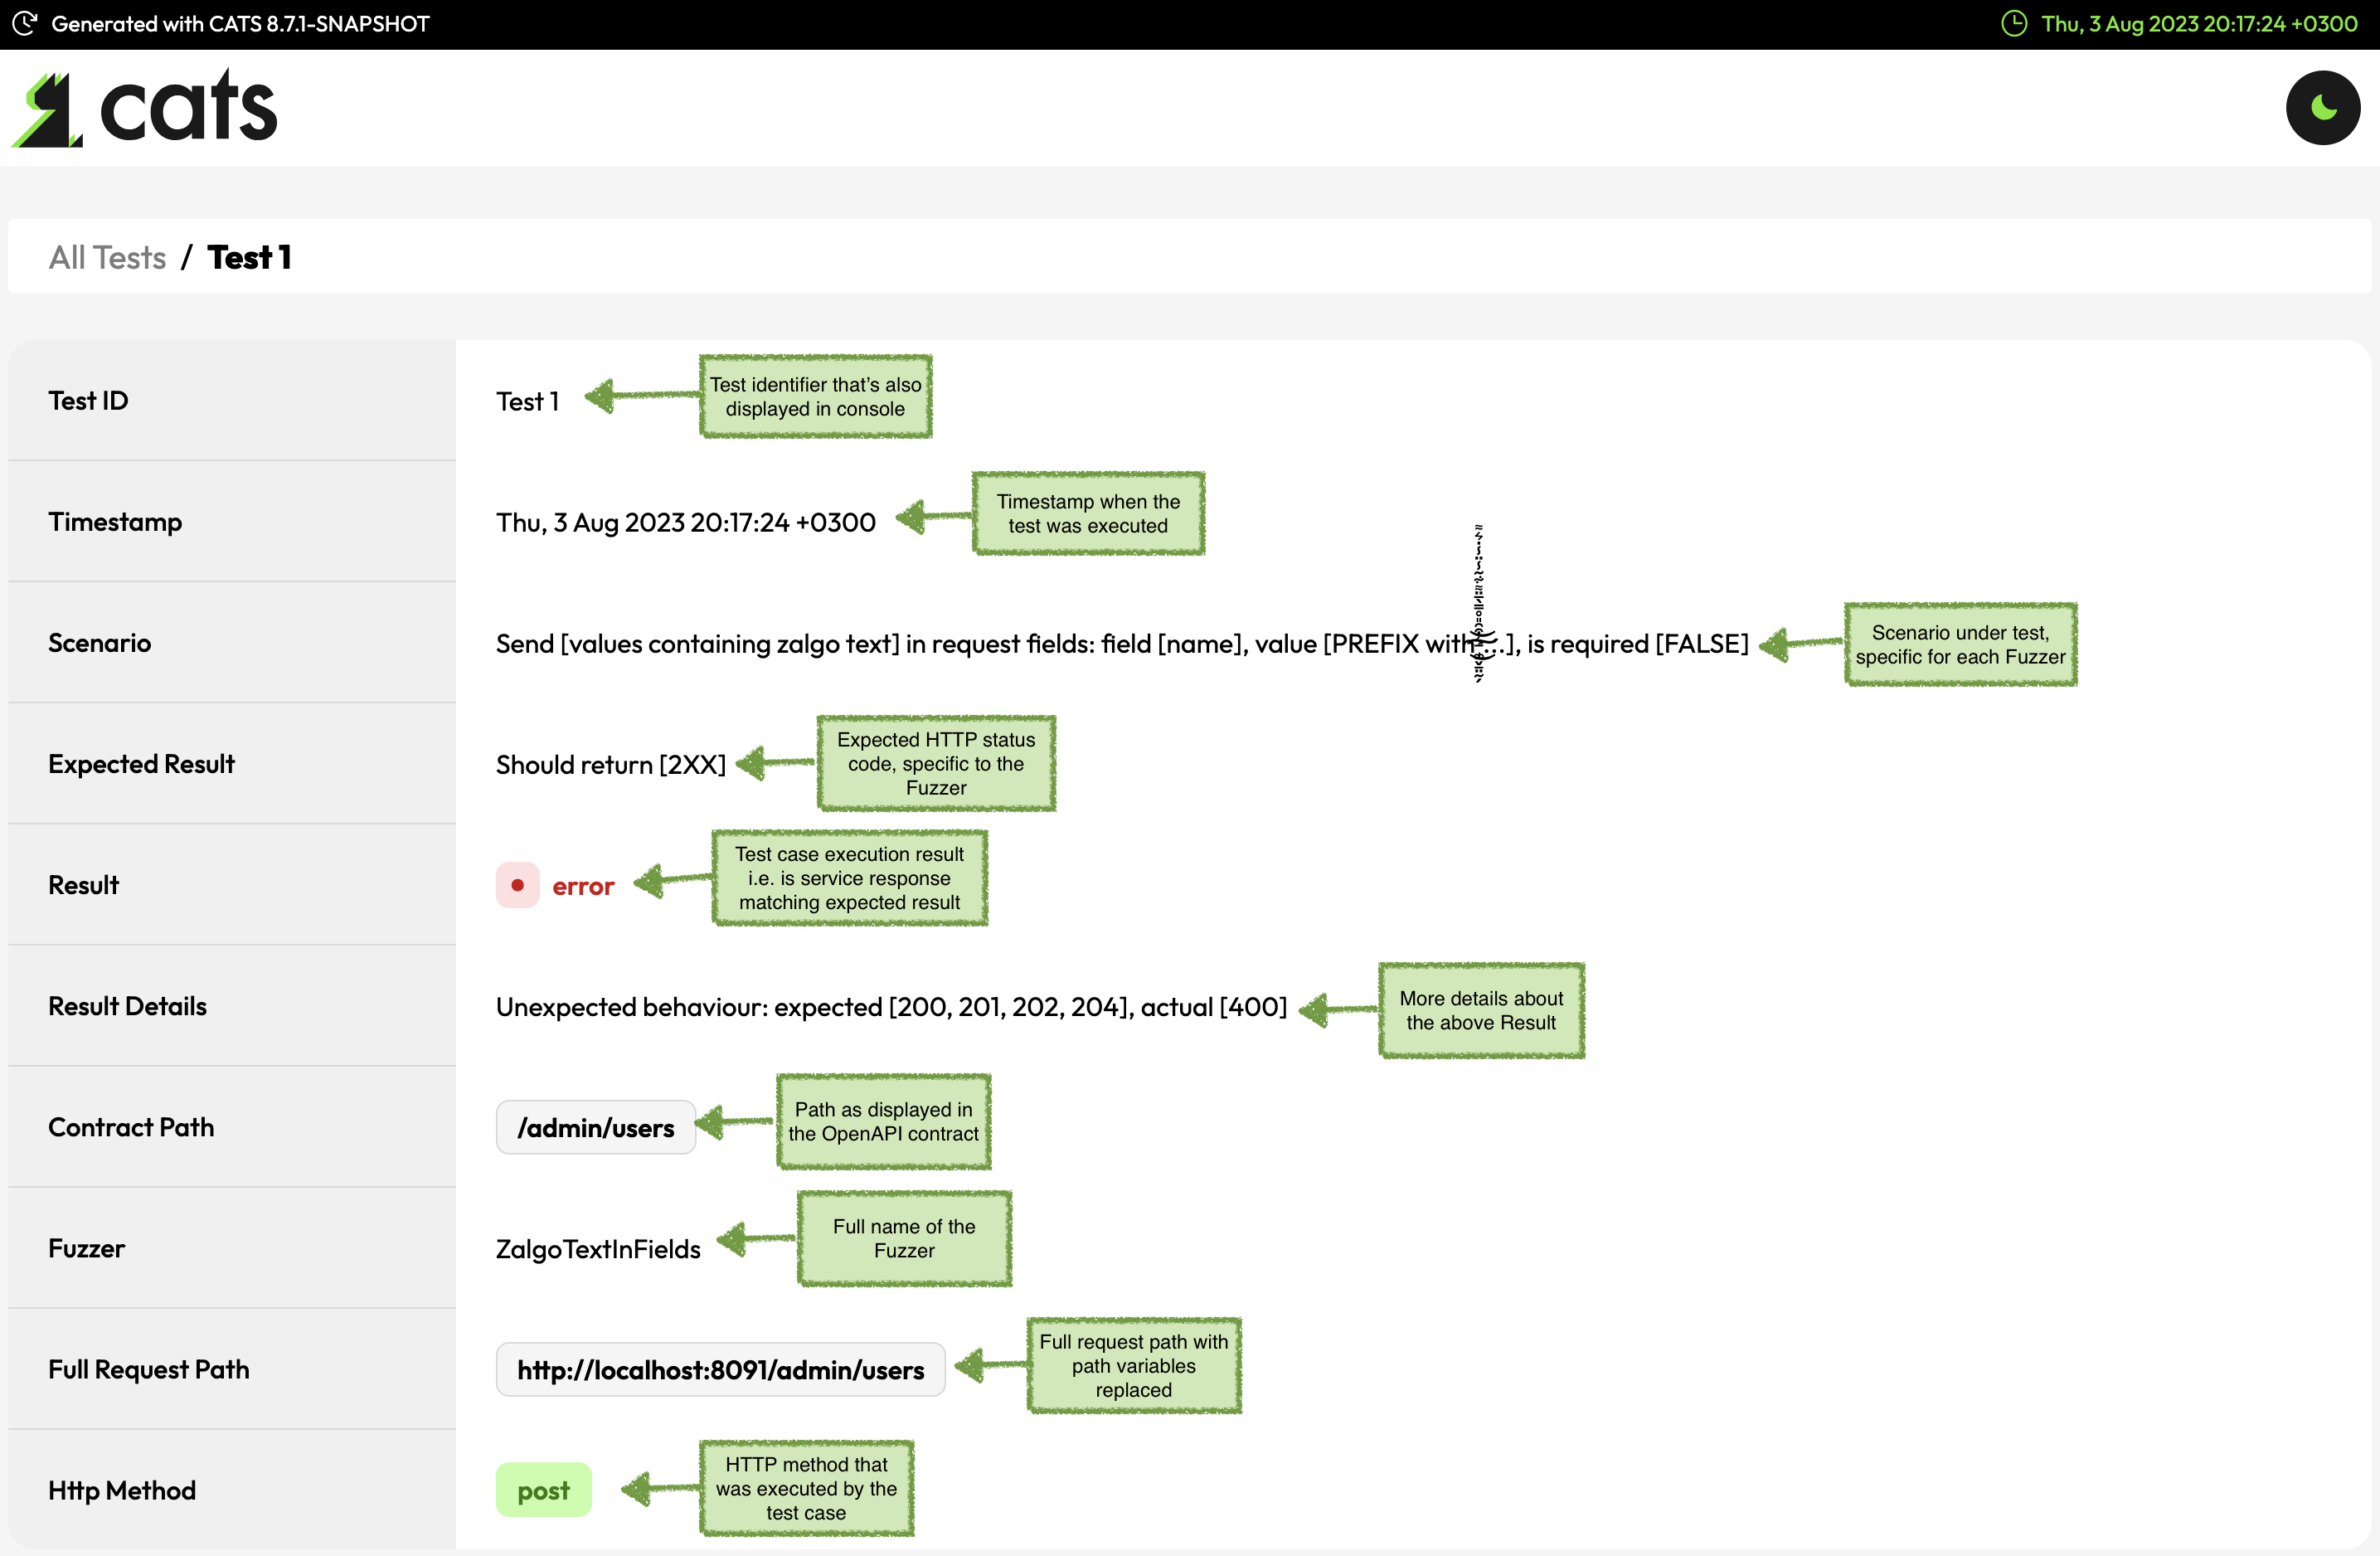
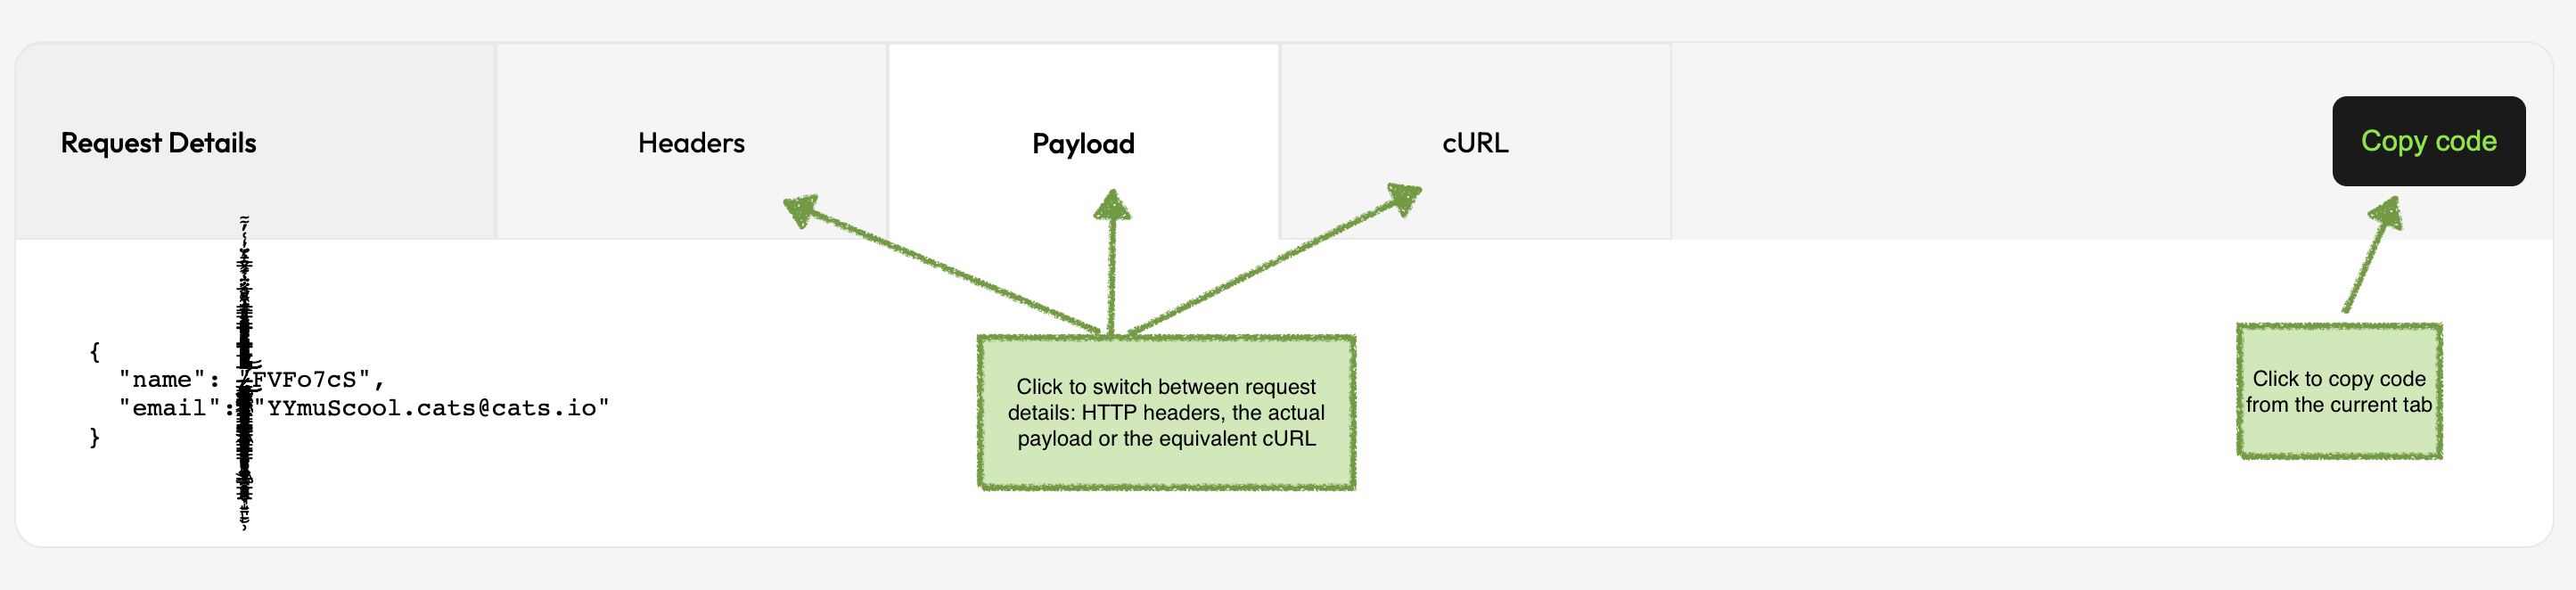
- have ability to click on any tests and get details about the Scenario being executed, Expected Result, Actual result as well as request/response details
You can change cats-report to something else using the -o argument. cats ... -o /tmp/reports will write the CATS report in the /tmp/reports folder.
Please note that Javascript might not play well with the CI servers. You may choose the non-JS version when embedding the report into a CI pipeline.
Along with the summary from index.html each individual test will have a specific TestXXX.html page with more details.
Individual tests are also written as JSON files. This is useful when you want to replay a test using cats replay TestXXX.
Tests can be uploaded as test evidence and be later reproduced/verified.
Understanding the Result Reason values:
Unexpected Exception- reported aserror; this indicates a possible bug in the service or a corner case that is not handled correctly by CATSNot Matching Response Schema- reported as awarn; this indicates that the service returns an expected response code and a response body, but the response body does not match the schema defined in the contract (validated using full OpenAPI 3.0/3.1 JSON Schema validation, including format assertions and$refresolution, unless--ignoreResponseBodyCheck/--ibis set)Undocumented Response Code- reported as awarn; this indicates that the service returns an expected response code, but the response code is not documented in the contractUnexpected Response Code- reported as anerror; this indicates a possible bug in the service - the response code is documented, but is not expected for this scenarioUnexpected Behaviour- reported as anerror; this indicates a possible bug in the service - the response code is neither documented nor expected for this scenarioNot Found- reported as anerrorin order to force providing more context; this indicates that CATS needs additional business context in order to run successfully - you can do this using the--refDataand/or--urlParamsargumentsResponse time exceeds max- reported as anerrorif the--maxResponseTimeInMsis supplied and the response time exceeds this numberResponse body truncated- reported aswarnwhen a response body exceeds--maxResponseBytes(default10485760bytes) and is truncated before body-dependent checks can completeCall timeout exceeded- reported aserrorwhen an HTTP call exceeds the configured--callTimeoutbudget (response code959)Response content type not matching the contract- reported aswarnif the content type received in response does not match the one defined in the contract for the received http response codeError details leak- reported aserrorif the response body contains sensitive informationNot Implemented- reported aswarnif response code is501Mass Assignment vulnerability detected- reported aserrorif the service allows mass assignment (includingReadOnlyFieldsMassAssignmentFuzzerwhen areadOnly: truefield sent in a write request is accepted and reflected)Path traversal vulnerability detected- reported aserrorbyPathTraversalInStringFieldsFuzzerwhen a response discloses local file content (such as/etc/passwd,win.ini, or/proc/self/environ) or leaks unmasked filesystem exception pathsHTTP method override accepted- reported aserrorbyHttpMethodOverrideTunnelingFuzzerwhen aPOSTcarrying an HTTP method-override header (X-HTTP-Method-Override,X-Method-Override,X-HTTP-Method) executes an undocumented verb such asDELETEInconsistent arithmetic total accepted- reported aserrorbyArithmeticTotalMismatchFieldsFuzzerwhen a write request with a contradicting total (such asunitPrice * quantity != totalAmount) is accepted with2XXand reflects the tampered totalPath and body ID mismatch accepted- reported aserrorbyPathBodyIdMismatchFuzzerwhen a write request whose top-level body identifier contradicts the URL{path}identifier is accepted with2XXand reflects the mismatched body identifierPATCH wiped omitted optional fields- reported aswarnbyPatchOmittedFieldsClobberFuzzerwhen a partialPATCHomitting a previously populated optional field causes that field to becomenull, blank, or missing on a subsequentGETPagination limit ignored- reported aswarnbyPaginationLimitHonoredFuzzerwhen aGETcollection request specifyinglimit=1(orsize=1/pageSize=1/per_page=1) returns more than1itemServer error with injection payload- reported aserrorif the service returns a server error for an injection payloadSSRF payload reflected in response- reported aserrorif the service is vulnerable to SSRF attacksCloud metadata service accessed- reported aserrorif the service leaks cloud metadataFile content exposed via SSRF- reported aserrorif the service leaks file content via SSRFSensitive data leak- reported aserrorif the service leaks sensitive dataNetwork error reveals SSRF attempt- reported aserrorif the service is vulnerable to SSRF attacksDNS resolution error reveals SSRF attempt- reported aserrorif the service is vulnerable to SSRF attacksHTTP client error reveals SSRF attempt- reported aserrorif the service is vulnerable to SSRF attacksInternal target reflected in response- reported aserrorif the service is vulnerable to SSRF attacksMissing recommended security headers- reported aserrorif the http response does not have the recommended security headersMissing response headers- reported aserrorif the http response does not contain all the headers defined in the contractHeuristic IDOR signal detected- reported aserrorwhen a request with a modified identifier returns2XXand the response contains the alternative identifierServer error with IDOR payload- reported aserrorif the service returns5XXfor an IDOR payloadWriteOnly fields exposed in response- reported aserrorbySensitiveDataExposureFuzzerwhen a response contains fields markedwriteOnlyin the OpenAPI contractSensitive data exposed in response- reported aswarnbySensitiveDataExposureFuzzerwhen a response contains undeclared fields with sensitive names (such aspassword,secret, orapiKey) and unmasked valuesRead broken after fuzzing- reported aserrorbyCheckReadsStillWorkFuzzerwhen an operation that returned2XXfor unmodified requests earlier in the run returns a5XXserver error after the path was fuzzedPUT retry caused server error,PUT retry rejected,PUT retry broke resource read,PUT is not idempotent- reported byPutIdempotencyFuzzerwhen repeating an identicalPUTfails or changes stable resource statePossible update/read inconsistency- reported aswarnbyUpdateReadConsistencyFuzzerwhen writable primitive fields sent in a successfulPUT/PATCHdiffer on a subsequentGETStale If-Match accepted,Stale If-Match caused server error,Conditional GET ignored,Conditional GET caused server error- reported byConditionalEtagFuzzerwhenIf-None-Matchor staleIf-Matchpreconditions are ignored or cause5XXerrorsCreated resource unavailable- reported aswarnbyCreatedResourceLocationFuzzerwhen aPOST201Locationreturns404or410onGETPotential cross-parent resource exposure,Cross-parent request caused server error- reported byCrossParentResourceIsolationFuzzerwhen a child resource is exposed or causes5XXunder a swapped parent IDEmpty reply from server,Connection refused,Read timeout,Write timeout,Connection timeout,HTTP protocol exception,Connection reset- explicit I/O error reasons corresponding to9XXcommunication codes
This is what you get when you click on a specific test:
You can generate multiple report formats in a single run by passing a comma-separated list to --reportFormat (for example --reportFormat HTML_JS,HTML_JS_CLUSTERS,JUNIT,WFC_REPORT).
HTML_JS_CLUSTERS
HTML_JS_CLUSTERS generates an interactive clustered HTML report (index.html) that groups failing and warning tests into root-cause clusters using response status, JSON error-message extraction, and response similarity (including 2XX validation errors).
HTML_ONLY
This format is similar with HTML_JS, but you cannot do any filtering or sorting. This is more suitable when embedding the CATS report into a CI pipeline.
JUNIT
CATS also supports JUNIT output. The output will contain one testsuite per fuzzer. Each test run by that fuzzer will be recorded as a testcase.
As the JUNIT format does not have the concept of warning the following mapping is used:
- CATS
errorwith valid HTTP codes are mapped as JUNITfailure - CATS
errorwith code 9XX are mapped as JUNITerror - CATS
warnis reported as JUNITskippedand message starting withWARN -
The JUNIT report is written as junit.xml in the cats-report folder. Individual tests, both as .html and .json will also be created.
WFC_REPORT
WFC_REPORT generates a standardized Web Fuzzing Commons report.json file in the report directory, mapping CATS findings to official WFC DefinedFaultCategory constants and CatsWfcFaultCategory sub-categories, suitable for cross-fuzzer benchmarking and WFC-compatible tooling.
If you want to have history for CATS runs you can use the --timestampReports argument. This will create sub-folders for each run within the cats-reports folder with the corresponding timestamp.
Triaging Reports & Verifying Fixes (cats triage)
To turn a cats-report folder into deduplicated root-cause clusters, remediation artifacts, and live fix verifications, run cats triage (aliases diagnose, doctor):
# Cluster errors by root cause and export remediation artifacts
cats triage -r cats-report -c openapi.yml \
  --export-refdata refData.yml \
  --export-correlations correlations.yml \
  --export-contract-patch contract-patch.yml \
  --export-reproducers reproducers.sh

# Replay 1 representative request per root-cause cluster against the live server to check FIXED vs STILL_FAILING vs INCONCLUSIVE
export Authorization='Bearer eyJ...'
cats triage -r cats-report --verify -s http://localhost:8080
cats triage classifies failures into prioritized root-cause categories (SERVER_CRASH_5XX, FIELD_DOMAIN_CONSTRAINT_4XX, CROSS_FIELD_CONSTRAINT_4XX, HEADER_CORRELATION_COLLISION, AUTH_CONFIGURATION_GAP, VALIDATION_BYPASS_2XX, UNRESOLVED_PATH_PARAM_404, UNRESOLVED_BODY_REFERENCE_404, ROUTE_NOT_FOUND_404, SUSPICIOUS_CORRELATION_404, RESOURCE_POOL_DEPLETED_404, and CONTRACT_MISMATCH).
2XX and Warning Tests When TriagingDo not pass --srs (--skipReportingForSuccess), --srw (--skipReportingForWarning), or -k (--skipReportingForIgnoredCodes) on runs you plan to triage or replay with cats replay --stateful—those flags omit the 2XX producer exchanges and warnings that --export-refdata, --include-warnings, and --stateful replay rely on.
Execution summary
Recent reports also include the active fuzzer profile (--profile), configured
quality-gate status, stop-condition status, and execution summaries. A run can
stop before all generated tests are executed because of --stopAfterTests,
--stopAfterErrors, or --stopAfterTimeInSec; tests already executed remain
included in the summary.